A pentest is a snapshot.
Networks change every day: a new printer here, a forgotten test server there, an update left pending for months. An annual pentest sees exactly one day of that — everything after it stays in the dark.
Each box represents one week of the year.
Argus24 checks every day —
all on its own.
Four steps, every single day. Nobody has to maintain lists or start scans by hand.
Discover
Finds every device on the network — from servers to refrigeration controllers, without you maintaining IP addresses.
Assess
Detects what is running on a device and automatically selects the right testing tools.
Compare
Compares each run with the previous one: What is new, what was fixed, what remains?
Report
Raises the alarm by email as soon as things get serious — and delivers reports for your documentation.
Proven tools,
one clear result.
Argus24 does not reinvent testing. It makes targeted use of the security industry's established tools — and translates their results into a common, understandable language.
Inventory
Finds devices and open services.
Known vulnerabilities
Known security gaps and misconfigurations.
Emerging vulnerabilities
Detection rules for newly disclosed vulnerabilities — updated daily.
Web applications
Security of web applications and web servers.
Systems & controllers
Refrigeration, heating, air conditioning, controllers — tested with particular care.
Accounts & permissions
Checks your Active Directory — read-only.
Web servers get web checks, domain controllers an identity check — automatically, matched to each device.
OT stands for Operational Technology: technology that controls physical equipment — refrigeration, heating, ventilation, building automation, production. Such devices are often sensitive and stay in service for years without updates; that is why Argus24 tests them with particular care.
You see at once what has changed.
Every finding is also mapped to the international reference list for web risks.
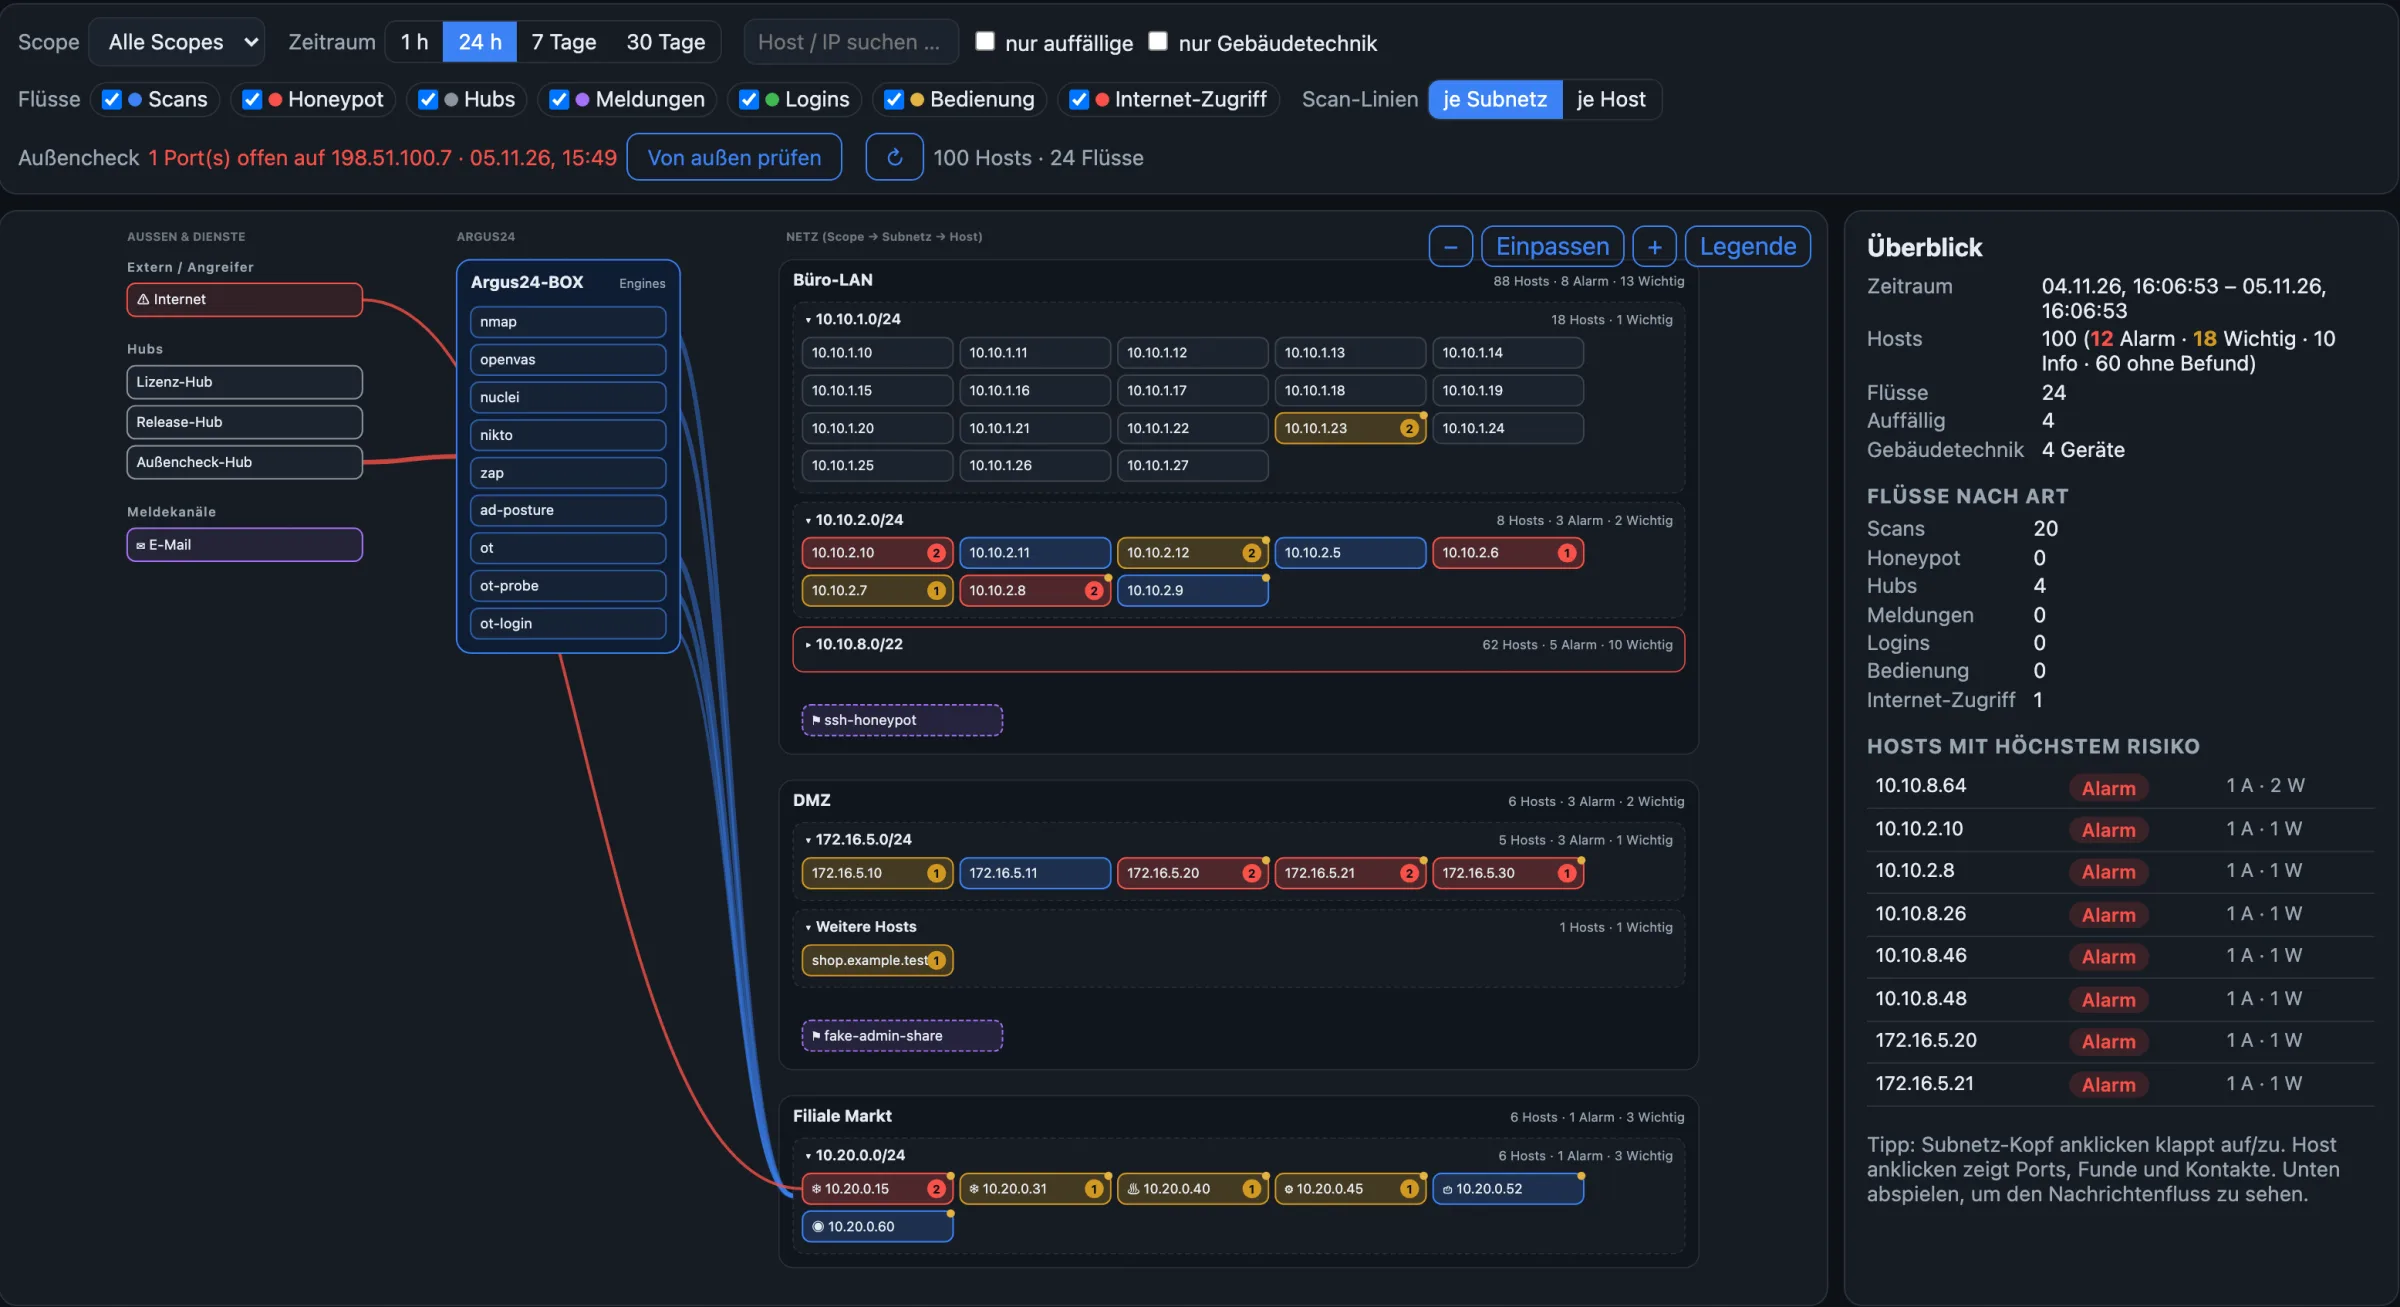
The network map shows where things are on fire.
At a glance
Every device color-coded by risk, with its device type — sorted by network and subnet.
Who talks to whom?
Scans, decoy hits, alerts — and, in red, whatever is reachable from the internet.
What happened?
Play back the last hours or days — and jump straight to the next anomaly.
Decoys that give attackers away.
Scanners find vulnerabilities — a honeypot catches the attacker. Argus24 sets out decoys that nobody needs in day-to-day operations. Anyone who touches them has no business there: every contact is an instant alarm, with practically no false alarms.
If the access comes from your own network, Argus24 points directly to the affected device — a typical sign of an attacker who is already moving through the network.
The decoys run on a separate, fully isolated device — cleanly separated from the production network.
Fake servers
Deceptively real services such as SSH, SMB, RDP or admin interfaces.
Tempting documents
Files and canary tokens that raise an alarm the moment they are opened.
Seemingly old accounts
A honey account in AD that looks attractive — but has no real permissions at all.
Even the refrigerated display case is a computer.
In the fall of 2026, refrigeration systems in hundreds of supermarkets were heated up remotely — via controllers whose user interface was reachable from the internet. Argus24 now specifically keeps an eye on such devices.
Recommendation: remove the port forwarding on the router; remote maintenance via VPN only.
What kind of device is it?
Refrigeration, heating, air conditioning, building automation, controllers, printers, cameras — with manufacturer and model.
Where is it vulnerable?
Known vulnerabilities of exactly these devices — and, on request, whether the factory default password still works. Password tests only with your authorization.
Is it reachable from the internet?
Daily via the SinCera hub. If so: immediate alarm. No findings leave your network in the process — the hub only sees what anyone on the internet can see anyway.
Not just the network — the identities, too.
Pure network scanners find open ports and CVEs, but not the class of error behind the most serious incidents: forgotten but still enabled, over-privileged domain accounts. A read-only AD module checks the identity hygiene of your Active Directory — and cross-checks which accounts are allowed to log on to DMZ-exposed hosts. It reports, but changes nothing.
Argus24 at work.
Illustrative preview of the interface — findings, history, identity posture and deception in a single view.
For larger screens
The interactive preview — findings dashboard, history, identity posture and the forensic CVR replay — is designed for larger screens. Please view it on a tablet or desktop (900 px wide or more).
Open on tablet or desktop| 10.0.12.18 | Default creds web login | Critical | new |
| 10.0.30.14 | Outdated OpenSSH | High | new |
| 172.16.8.9 | Anonymous FTP | High | recurring |
| 192.168.40.7 | TLS 1.0 enabled | Medium | recurring |
- svc-idx-backupno login for 183 daysStale + Enabled
- adm-legacy01Domain AdminsOver-privileged
- websvc-appSPN setKerberoastable
- test-tempDMZ logon allowedDMZ-exposed
- SERVICESSH login attempt · decoy-dmz-012 min ago
- ACCOUNTHoney-Account svc-idx-backup14 min ago
- FILEDecoy file Passwords_2024.xlsx1 hr ago
- SERVICEMSSQL connection · decoy-dmz-023 hrs ago
Forensic replay (CVR) — play back the communication between components with exact timing and jump to the next anomaly:
Illustrative mockups · final interface may differ
We only test
what you authorize.
Written authorization
Every network segment needs a signed engagement — otherwise no testing. Expired means: no scan.
Clear boundaries
You define IP ranges, time windows and testing depth yourself.
No attacks
Argus24 finds vulnerabilities but never exploits them. Password tests only with your authorization.
Emergency stop
One click immediately stops all running and scheduled tests.
Relocation guard
On an unknown network, the box pauses until you confirm the network.
Logging and roles
Every action recorded in a tamper-proof log, permissions based on role.
Under the hood: every target is checked against the allowlist and global denylist before every run · append-only audit log · self-hosted — your data stays with you.
Up and running in three steps.
Define the scope
Specify authorized target ranges and bind them to an authorization record.
Choose policy & schedule
Configure engines, intensity and scan windows — once set up, it runs on its own.
Monitor & respond
The platform scans automatically, shows changes and raises alerts on critical findings.
Built for continuous accountability.
IT security service providers
Continuous client monitoring between the major audits — with auditable reports.
Internal security & IT teams
A permanent view of your own attack surface instead of annual spot checks.
Compliance environments
A traceable, documented vulnerability history over time.
Full feature set —
everything on board.
✓ Platform & core
- Scope & authorization management
- Guardrail layer & tamper-proof audit log
- Discovery (naabu / nmap) & auto-pilot
- Normalization & diffing
- Mapping to OWASP Top 10:2025
- Network map with timeline & replay
- Relocation guard on network change
✓ Engines, modules & integration
- Greenbone / OpenVAS · Nuclei
- Web scans (ZAP / Nikto)
- 24/7 scheduling
- Reporting (PDF/CSV/JSON) & multi-channel alerting
- API & Dashboard · Login/SSO (Keycloak)
- AD / identity posture analysis
- Honeypot / deception detection
- Building technology / IoT detection & OT checks
- Factory default password check (only with authorization)
- Daily outside-in check via the SinCera hub
Prefer it turnkey?
As an appliance.
Argus24 is available as a ready-made appliance operated by SinCera — plug it in and it runs. Optionally complemented by a separate, fully isolated deception appliance.
One box on the network
As a small appliance or virtual machine. Nothing is installed on your devices.
New detection rules every day
Test templates for newly disclosed vulnerabilities update themselves every day.
Reports & alerts
Reports as PDF, CSV and JSON; instant email alerts for critical findings and decoy hits.
Turnkey
Plug it in and it runs. No installation on your side, no waiting for spare capacity in your IT team.
Managed by SinCera
We handle setup, configuration, updates and monitoring — you have nothing to administer.
High-quality 24/7 hardware
Designed for true continuous operation: reliable, quiet and compact, around the clock.
Signed, automatic updates
Updates arrive verified and signed, with automatic rollback if problems occur — no downtime, no action required from you.
Encrypted & sealed
Disk encryption and a tamper-proof seal protect the device against unnoticed tampering.
Full data sovereignty
Self-hosted on your premises — findings and data never leave your network.
Proactive monitoring
We keep an eye on health, license and update status and get in touch before anything gets stuck.
Fast commissioning
Installation by our technicians, including acceptance testing and complete documentation at handover.
Predictable costs
A fixed monthly or annual flat fee, license included — no surprises.
Replacement when needed
If a device fails, we take care of a fast replacement; your protection keeps running.
Argus24 Appliance
The complete platform as a ready-to-run device — set up, kept up to date and monitored by SinCera. Plug it in and you are protected.
Deception appliance
A separate, fully isolated decoy sensor. It provides deceptively real services; every interaction is an instant alarm — cleanly separated from the production network.
No SOC? Argus Cloud.
Honeypot Air is a compact deception sensor (“canary”) for small and micro businesses — the shop around the corner, the medical practice, the law firm, the trades business.
- ▸Decoys on the network — every touch is an alarm. Hardly any false alarms, no configuration.
- ▸No local Argus24 box. Control & alerting run entirely through the Argus Cloud.
Let's look at your network
together.
In a short meeting, we show you Argus24 live — directly on your network if you wish.
Book a meetingArgus24 — A product of SinCera Tech GmbH · Continuous security testing